Contoso, Ltd. is a consulting company that has a main office in San Francisco and a branch office in Dallas.
Contoso has a hybrid environment that contains on-premises servers connected to Azure, a Microsoft 365 E5 subscription, and an Azure subscription named Sub1.
The on-premises network contains an Active Directory Domain Services (AD DS) forest that syncs with contoso.com. The forest contains a server named Server1 that runs Windows Server.
Segment
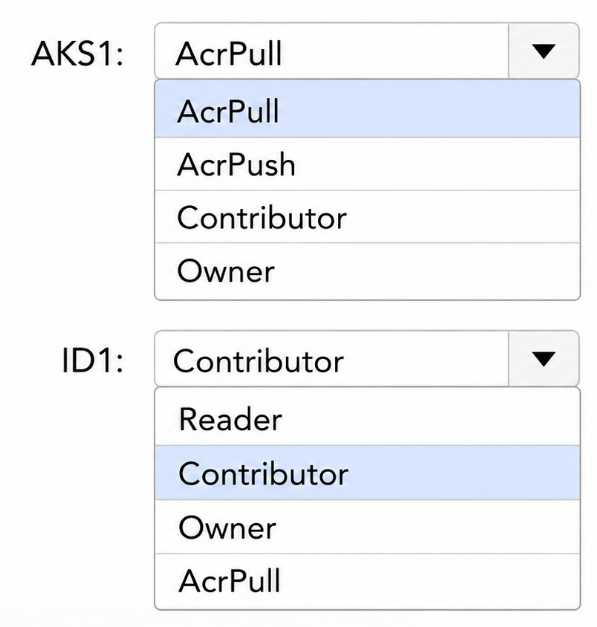
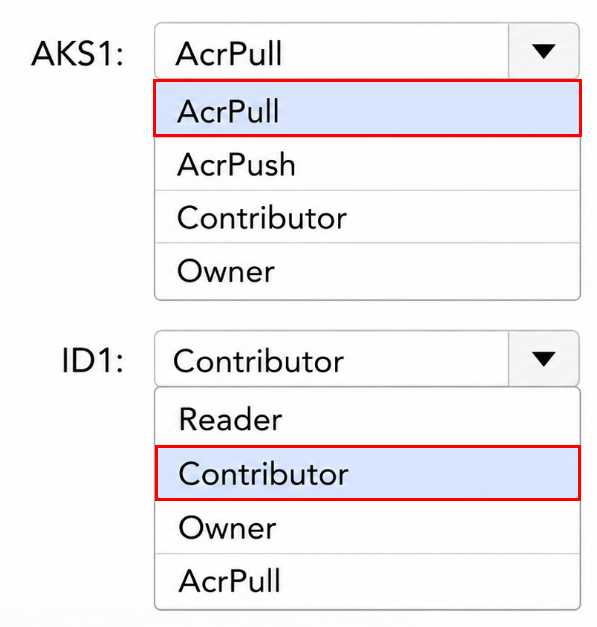
You need to configure the AKS1 and ID 1 managed identities to meet the technical requirements. The solution must follow the principle of least privilege.
Which role should you assign to each identity? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Reveal answer
Correct answer
Rate this question
No comments yet. Start the discussion.
Question 2 Contoso Ltd,
Multiple answer
You need to implement the planned change for SQLdb1
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point
A
Create a compliance policy.
B
Configure Microsoft Entra authentication for SQLServer1.
C
Create a Conditional Access policy.
D
Configure federated client identity for SQLdb1.
E
Configure a user-assigned managed identity for SQLdb1.
Reveal answer
Correct answer
B
Configure Microsoft Entra authentication for SQLServer1.
C
Create a Conditional Access policy.
Explanation
Microsoft Entra authentication must be configured on the SQL server before Microsoft Entra identities and Conditional Access can govern database access. A Conditional Access policy then enforces the planned access control for SQLdb1. A compliance policy does not authenticate SQL connections. Federated client identity and a user-assigned managed identity are used for workload identity scenarios, not for enforcing user sign-in requirements against Azure SQL in this case. The exam objective emphasizes practical identity enforcement rather than cosmetic configuration. A valid answer must identify who authenticates, what permission is granted, where the scope is applied, and whether the method continues to work without passwords or secrets. That is why the selected answer is preferred over broader administrative roles or unrelated access settings. The result is a direct exam-style implementation choice: it changes the required security behavior without relying on unrelated monitoring, manual cleanup, or excessive privilege. Official Microsoft source/topic: SC-500 Study Guide > Azure SQL authentication and conditional access; Microsoft Learn > Microsoft Entra authentication for Azure SQL.
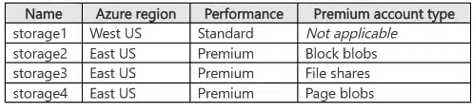
You need to implement the planned change for storage2 The solution must meet the technical requirements for storage encryption.
What should you do?
A
Enable purge protection for storage2.
B
Create an encryption scope in storage2.
C
Configure storage2 to use an account encryption key.
D
Assign an Azure role-based access control (Azure RBAC) role to storage2.
Reveal answer
Correct answer
B
Create an encryption scope in storage2.
Explanation
An encryption scope provides a named encryption boundary for blobs and can use Microsoft-managed or customer-managed keys depending on configuration. The planned change refers to storage encryption, and the visible answer set points to a storage2-specific encryption configuration rather than vault purge protection or Azure RBAC. Account-level encryption keys affect the entire account; encryption scopes are the correct more granular storage encryption control. The important exam skill is separating data-plane access, management-plane administration, and network reachability. A storage, database, or firewall setting must be selected because it enforces the exact path requested in the scenario. Distractors often look plausible because they improve security generally, but they do not satisfy the protocol, scope, or automation requirement stated in the question. The result is a direct exam-style implementation choice: it changes the required security behavior without relying on unrelated monitoring, manual cleanup, or excessive privilege. Official Microsoft source/topic: SC-500 Study Guide > storage encryption; Microsoft Learn > Azure Storage encryption scopes.
Getting the hang of it?
196 more SC-500 questions are waiting, each with its answer. Unlock them all
Question 4 Mix Questions
Drag and drop
Case study: Mix Questions
Mix QuestionsSC-500 Mix Questions IN THIS CASE STUDY
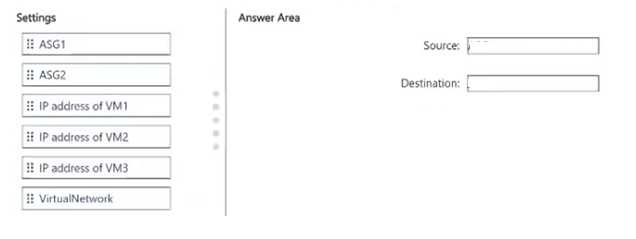
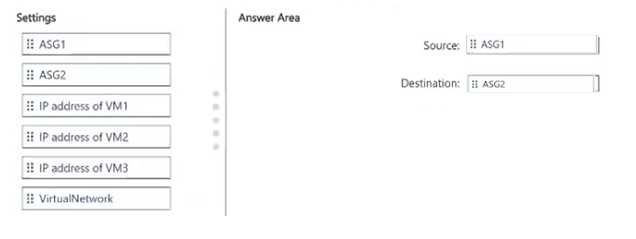
You have an Azure virtual network named VNet1 that contains three subnets named Subnet1, Subnet2 and Subnet3. A single network security group (NSG) named NSG1 is associated with all the subnets. You have the following virtual machines:
•VM1 on Subnet1
•VM2 on Subnet2
VM3 on Subnet3
You create two application security groups named ASG1 and ASG2. VM2 is a member of ASG1, and VM3 is a member of ASG2.
You need to ensure that only VM2 can connect to VM3. The solution must continue to work if the private IP address of VM2 changes.
How should you configure the inbound rule on NSG1 ? To answer, drag the settings to the correct configurations. Each setting may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Reveal answer
Correct answer
Rate this question
No comments yet. Start the discussion.
Question 5 Contoso Ltd,
Hotspot
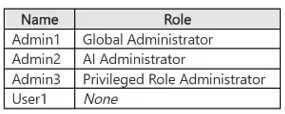
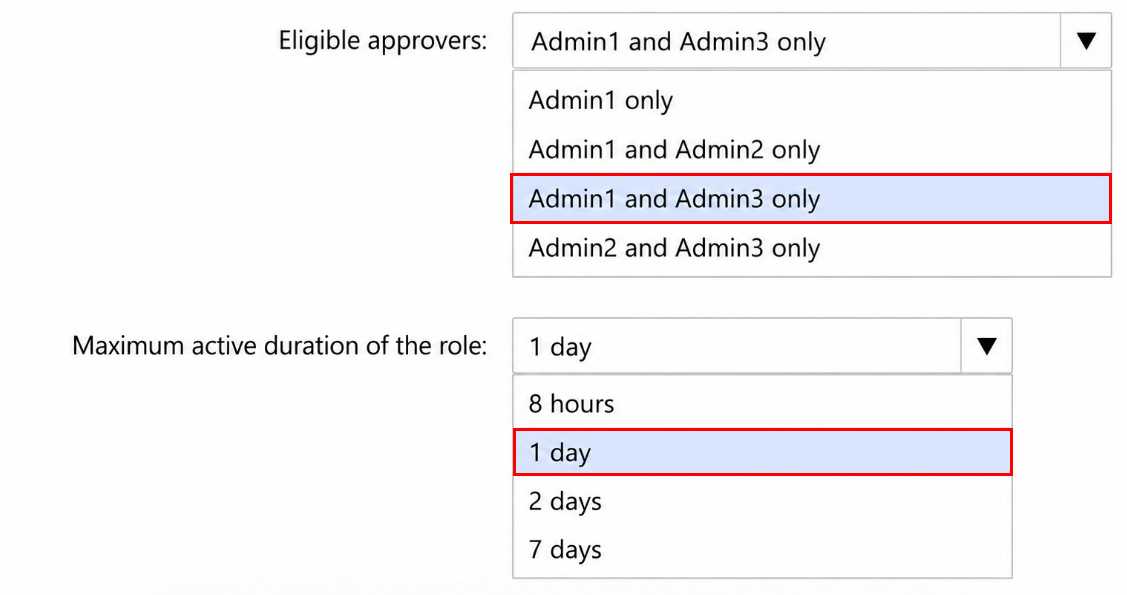
User1 has requested to use the AI Administrator role.
Which approvers can approve the request, and how long will User1 be an AI administrator after the role is approved? To answer, select the appropriate options in the answer area.